
New York AI Security and Data Protection Summit 2026
150+ data protection, privacy, security, and governance leaders. One room, one day. A fast-moving, peer-led summit on the pressures reshaping data protection and security: AI systems copying sensitive information into new environments, rising regulatory scrutiny, breach response, and growing third-party and cross-border risk. Free to attend. Register now.
Sensitive data is spreading faster than most protection programs can track it.
RAG pipelines, copilots, vector stores, prompt logs, SaaS platforms, and cloud environments are duplicating, caching, and moving sensitive information into places traditional privacy and security programs were never built to see.
At the same time, regulatory expectations are rising, third-party exposure is becoming harder to assess, and teams are being asked to support AI adoption without losing control of the data underneath it.
You are still expected to perform the same impossible balancing act: keep the business moving, reduce risk, satisfy regulators, and prove that the right controls are working at any moment.
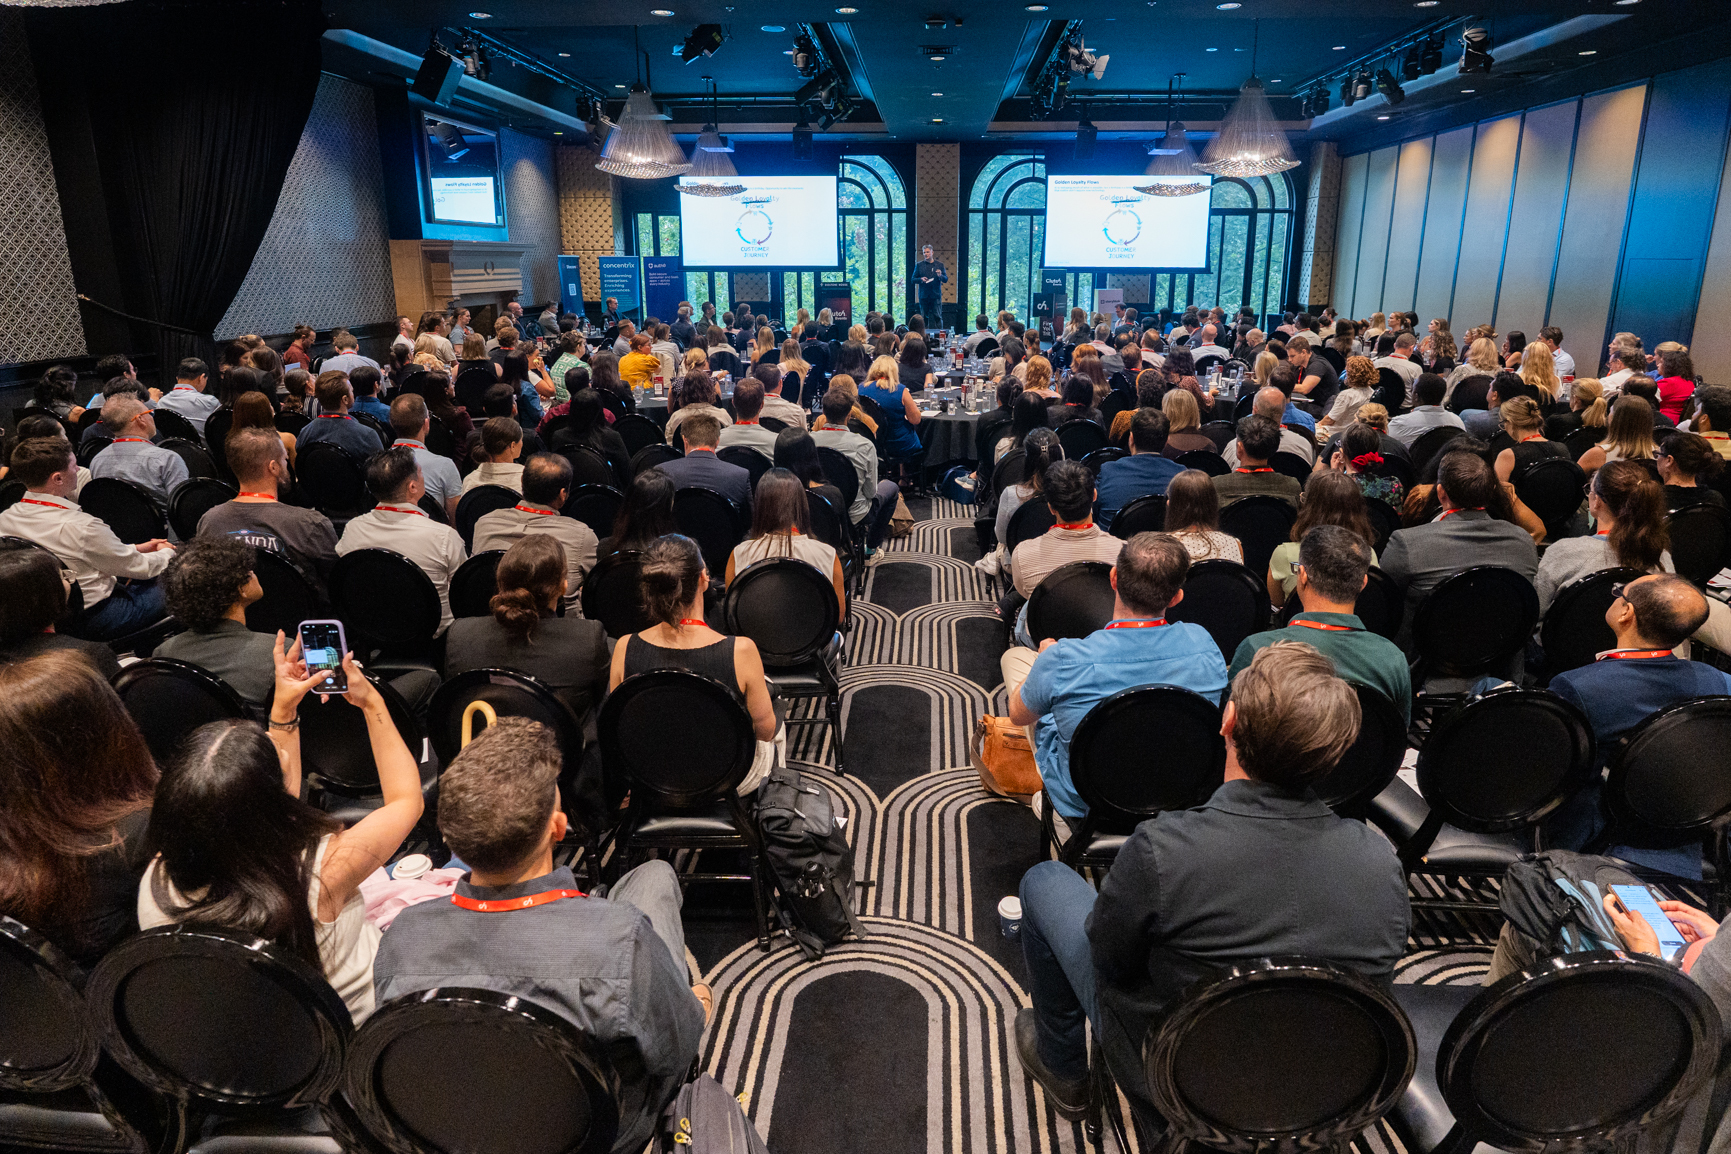
The New York AI Security and Data Protection Summit is a closed-door, practitioner-led event for the people carrying that responsibility every day. Privacy, security, governance, risk, legal, and data leaders come together to talk candidly about what is working, what is not, and what needs to change before today's blind spot becomes tomorrow's incident.
If you want to understand how your program compares with other leading organizations across New York, this is where you will find out.
This is not a conference you sit through. It is a working session with people facing the same pressures you are.
We keep it deliberately small and hands-on. The real value is in the conversations that are difficult to have anywhere else.
Here is how the day actually runs:
- Practitioner keynotes from people who have dealt with these challenges firsthand
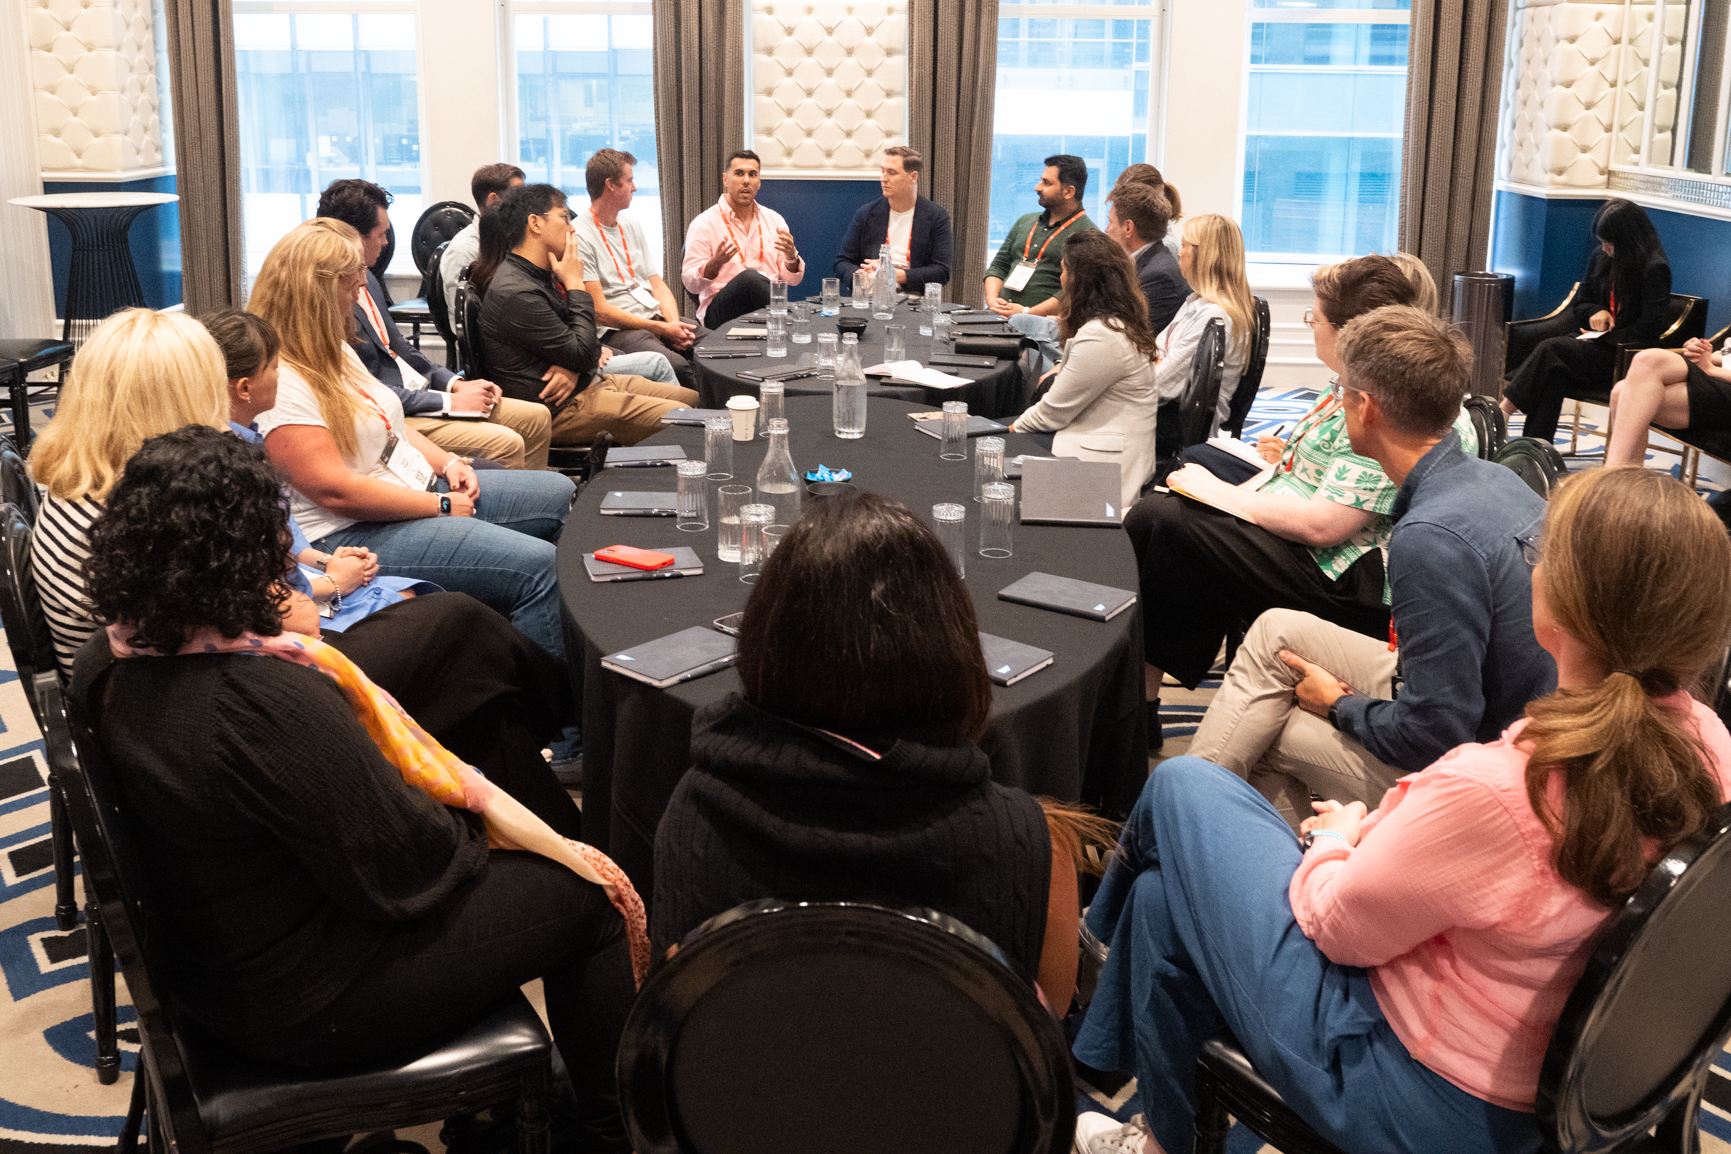
- Peer roundtables where you tackle real problems alongside people in similar roles
- Live scenarios the whole room works through together
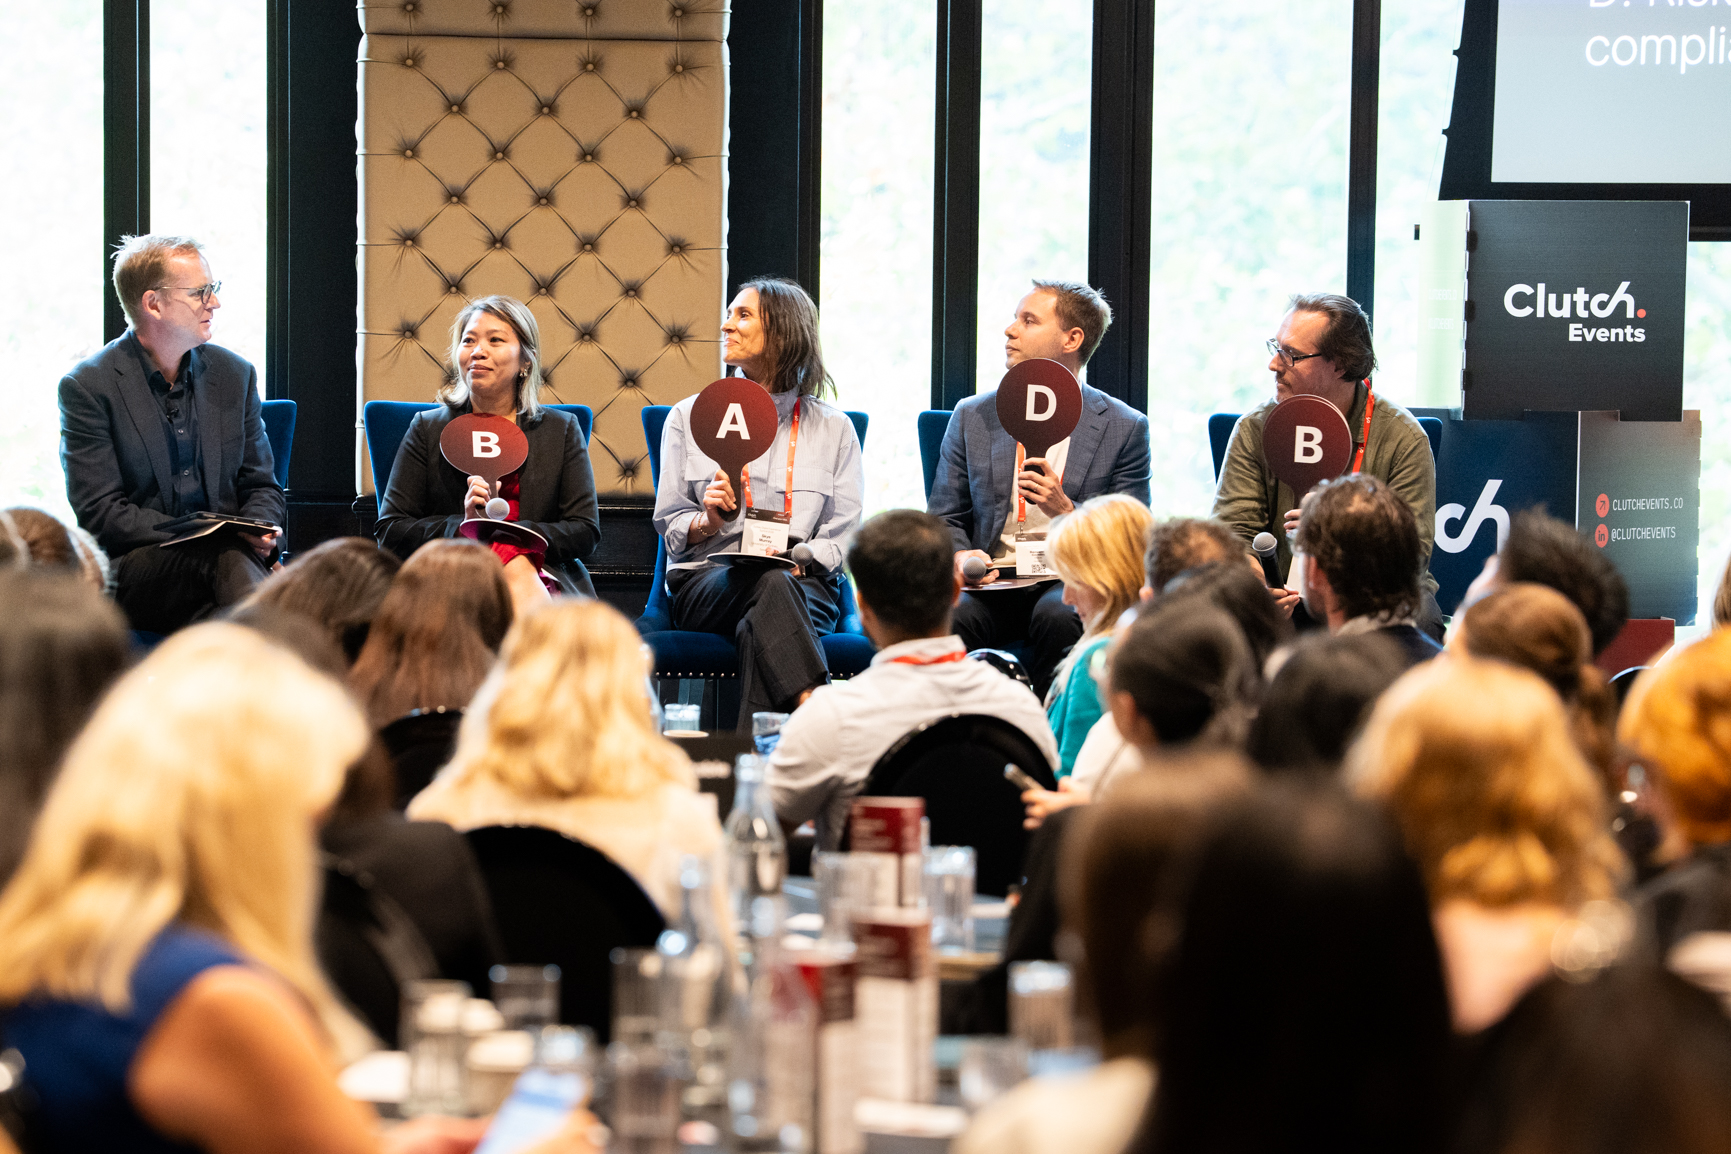
- Interactive panels you help steer from your phone
- Structured networking designed to lead somewhere
- Optional one-to-one meetings matched to your challenges
- Knowledge challenges and prizes to put your thinking to the test
Free to attend. No vendor pitching. Just a room full of people who understand the responsibility.
Register now to secure your seat.
Our Speakers






Agenda
Beat the rush and join us early for complimentary barista-made coffee and breakfast.
The hardest data security problem right now is not protecting the databases you know about. It is finding every place AI has quietly copied what was inside them.
RAG pipelines, copilots, vector stores, evaluation sets, and AI-powered SaaS all duplicate, cache, and log sensitive data faster than most teams can map it. Much of that data lands in systems traditional security programs were never built to inspect.
This keynote is a practical look at how teams regain visibility across an AI-enabled environment. Where sensitive data turns up, which copies are hardest to pin down, and how to reduce the blind spots before they become part of the next breach.
We’ll cover:
- Where sensitive data now hides, from vector stores and prompt logs to evaluation sets and SaaS AI features
- How to discover and classify AI-created copies without slowing adoption
- Practical ways to remove, restrict, or protect exposed data before it becomes an incident
Finding sensitive data is no longer enough. The harder question is whether you can prove it is governed.
Boards, auditors, and regulators want evidence. Who owns the data, who can reach it, how long it is kept, whether access is reviewed, and whether deletion really happened. In New York, this is moving from an operational expectation to signed accountability. Since November 1, 2025, DFS-covered entities have needed written policies for maintaining an inventory of their information systems, while annual Part 500 submissions are signed by the highest-ranking executive and the CISO.
This panel gets into what defensible data governance actually looks like, and why programs that stop at discovery often fall apart when someone asks for proof.
We’ll discuss:
- Moving from periodic discovery to continuous, evidence-based governance
- Proving retention, access reviews, and deletion are happening across cloud, legacy, and AI environments
- What senior leaders need to know before they put their names behind the organization’s controls
In this innovative session, attendees will be faced with a series of scenarios that they may face in their roles. Attendees will discuss the possible courses of action with their peers to consider the ramifications of each option before logging their own course of action.
Results will be tallied and analysed by our session facilitator and results will impact the way the group moves through the activity.
Will we collectively choose the right course of action?
Most teams think of AI data exposure as a search problem — find the copy, delete it, done. It isn't. A vector embedding is a derivative that behaves like your data: you can't search for it the way you'd search for a file, and deleting the source record doesn't remove it. Every eval set, cache, agent memory and vendor-side index adds another copy you'll never find that way.
Using the M365 Copilot rollout as the shared reference point, this session works through where the real leverage is: the decisions that create copies in the first place, not the cleanup afterward.
- Where copies actually get created — connector scope, index builds, retention defaults and derived-artifact deletion terms — and why these decisions matter more than any post-hoc search-and-delete effort.
- The two failure modes that keep showing up: permission inheritance that's technically correct but oversharing by synthesis, and source misconfiguration that was survivable before retrieval made it searchable in plain language.
- What to lock down before rollout, not after — using the M365 Copilot experience most of the room already lived through as the worked example.
Privacy and security protect the same data, but they do not start from the same question.
Privacy asks whether data should be collected, retained, or reused at all. Security asks who can reach it and how it should be protected. Once AI starts combining and repurposing enterprise data in ways nobody imagined when it was collected, those decisions can no longer be made in separate rooms.
This panel brings privacy and security leaders together to compare how they divide the work, where responsibilities overlap, and what happens when the two functions reach different conclusions.
We’ll discuss:
- How privacy and security divide ownership of minimization, retention, and deletion
- Preparing for new state privacy and AI rules without rebuilding controls market by market
- Telling one defensible story about your data practices to regulators, boards, and customers
Put your knowledge to the test in this fast-paced quiz covering real-world trivia, key concepts, and emerging trends. Compete for bragging rights—and a travel voucher—as the top scorer takes the crown.
Most enterprise Risk Appetite Statements are aspirational, qualitative policy documents that sit on a shelf until an auditor asks for them. They rarely tell a product team whether they can deploy an AI model, or tell procurement whether a vendor's risk profile is acceptable. Without real, quantitative inputs, leaders are left making reactive decisions in a vacuum.
This keynote explores how to turn the Risk Appetite Statement from static policy into a living, data-driven decision engine, feeding it integrated inputs across data privacy, information security, AI pipelines, and third-party ecosystems to transform abstract tolerance into clear thresholds that drive confident execution.
- How to feed your RAS quantitative, real-time inputs from across privacy, security, AI and third-party risk.
- How to convert abstract risk tolerance into concrete thresholds that give product and procurement clear go/no-go answers.
- How a living RAS shifts leaders from reactive decisions to confident, data-backed business execution.
As AI regulations multiply, many organisations are creating separate compliance programs for each new law. That approach is costly, slow, and difficult to sustain. This keynote explores how organisations can simplify compliance by building a single, high-standard control framework that meets multiple regulatory requirements at once. Learn how legal, privacy and security teams can work together to govern AI, reduce data risk, and create continuous evidence that stands up to regulators, boards and auditors.
- How to simplify overlapping AI, privacy and cybersecurity regulations with one unified compliance framework.
- Practical ways to govern AI data, reduce dark data, and strengthen data minimisation.
- How to build continuous evidence of compliance that satisfies regulators, auditors and boards.
Most incident response plans assume you can trace what data was involved. AI breaks that assumption.
Sensitive information may now sit in prompt histories, vector stores, evaluation sets, temporary caches, and third-party AI services that were never included in the original data map. When an incident happens, the first and hardest question becomes what was actually exposed.
This think tank brings security, privacy, legal, and data protection engineering leaders together to work through how breach response changes when AI is involved. In New York, that can mean reconciling the SHIELD Act with NYDFS and SEC requirements, while determining whether encryption held and whether the keys were also compromised.
We’ll discuss:
- Scoping what was exposed when data has been copied far beyond production systems
- Making disclosure calls across NYDFS’s 72-hour requirement, the SEC’s four-business-day deadline once a public company determines an incident is material, the SHIELD Act, and other state regimes
- How encryption, tokenization, and masking change the real exposure, and how to prove those controls held after an incident
Unwind with your peers for a couple of drinks on us.
Unwind with your peers for a couple of drinks on us!
Attending Companies








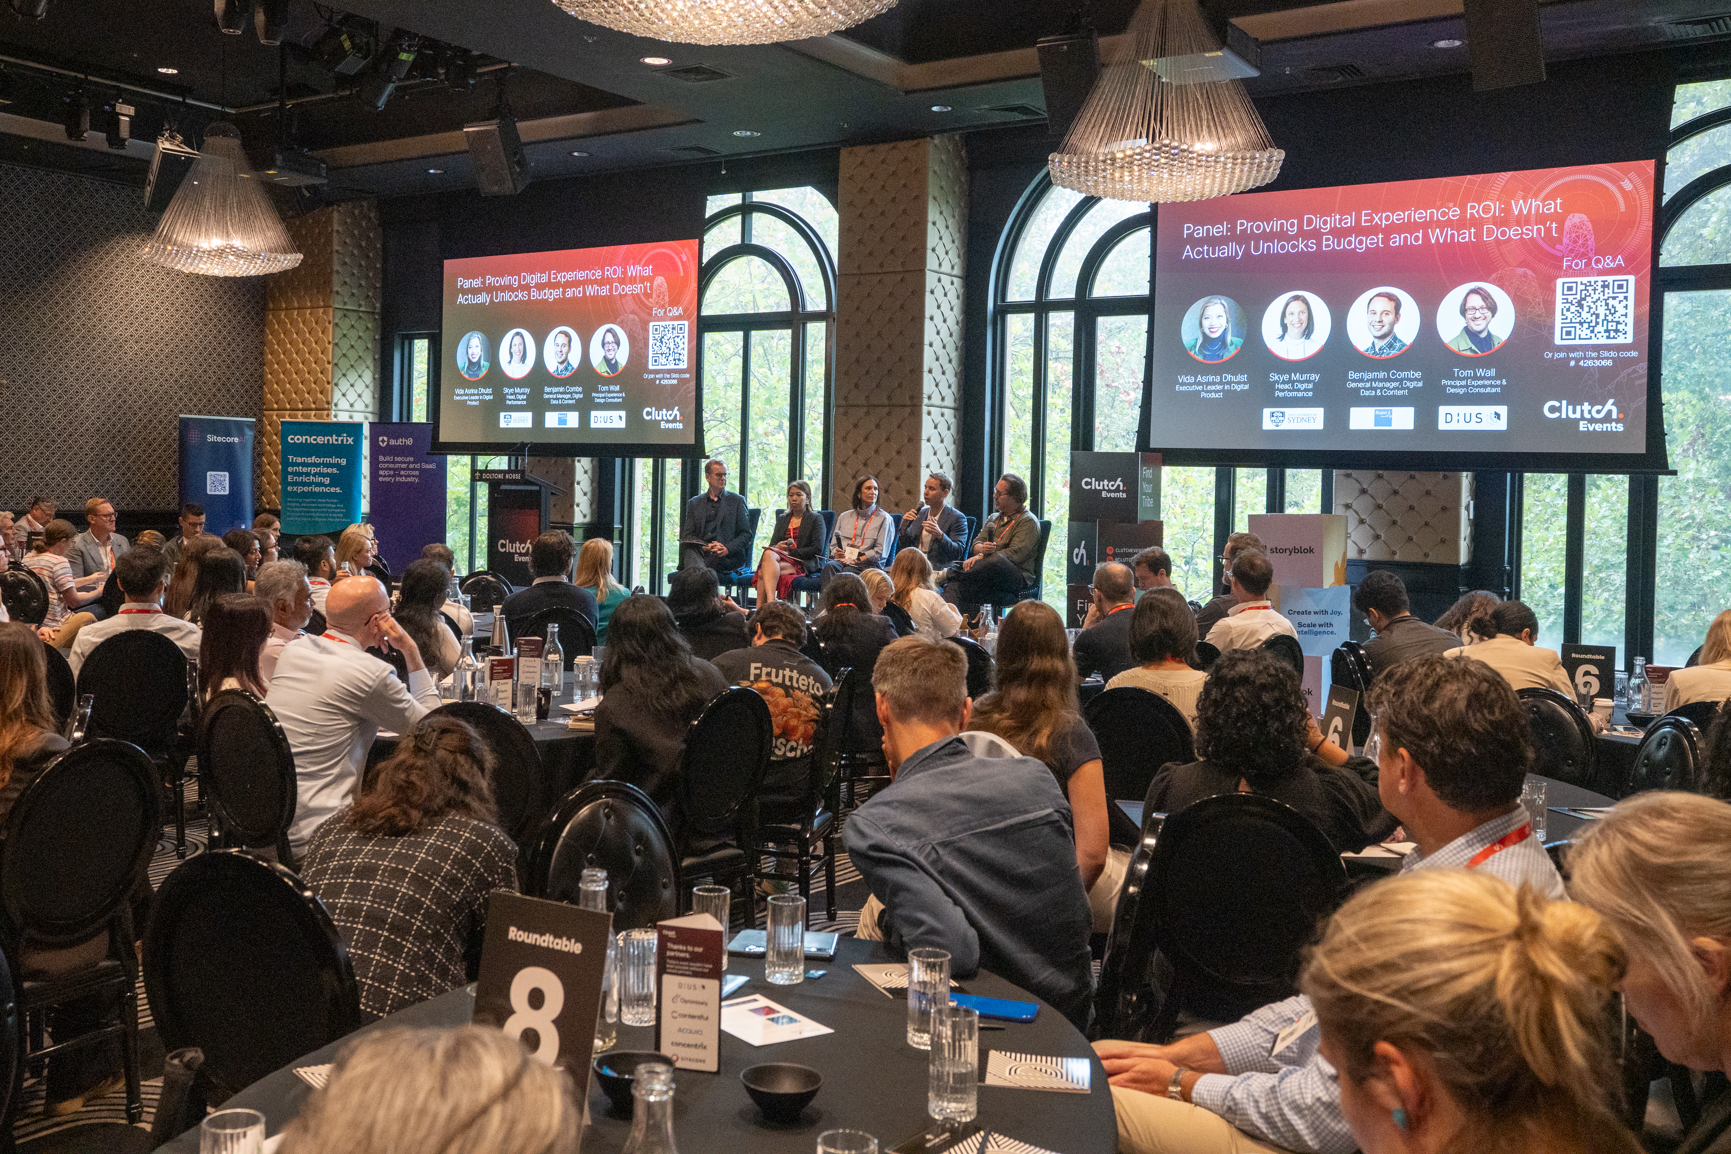
Attendee Testimonials
Session Highlights

AI Has Already Copied Your Data. Can You Still Find It? - Manoj S (Director, AI/ML & Security Architecture, TIAA)
Opening keynote: regaining visibility across vector stores, prompt logs, and AI-created data copies.
From Aspirational to Operational: The Data-Driven RAS - Maya Goethals (Director, Compliance & Operational Risk, Bank of America)
Keynote: turning the Risk Appetite Statement from static policy into a live, data-driven decision engine.
The Breach Involves AI. What Was Actually Exposed? - Willie Session (CISO, Booking Holdings Financial Services) & panel
Think tank: scoping exposure and disclosure across NYDFS, SEC, and SHIELD Act timelines.
Our event sponsors
Past Speaker Highlights
Past Sponsors

Event Location
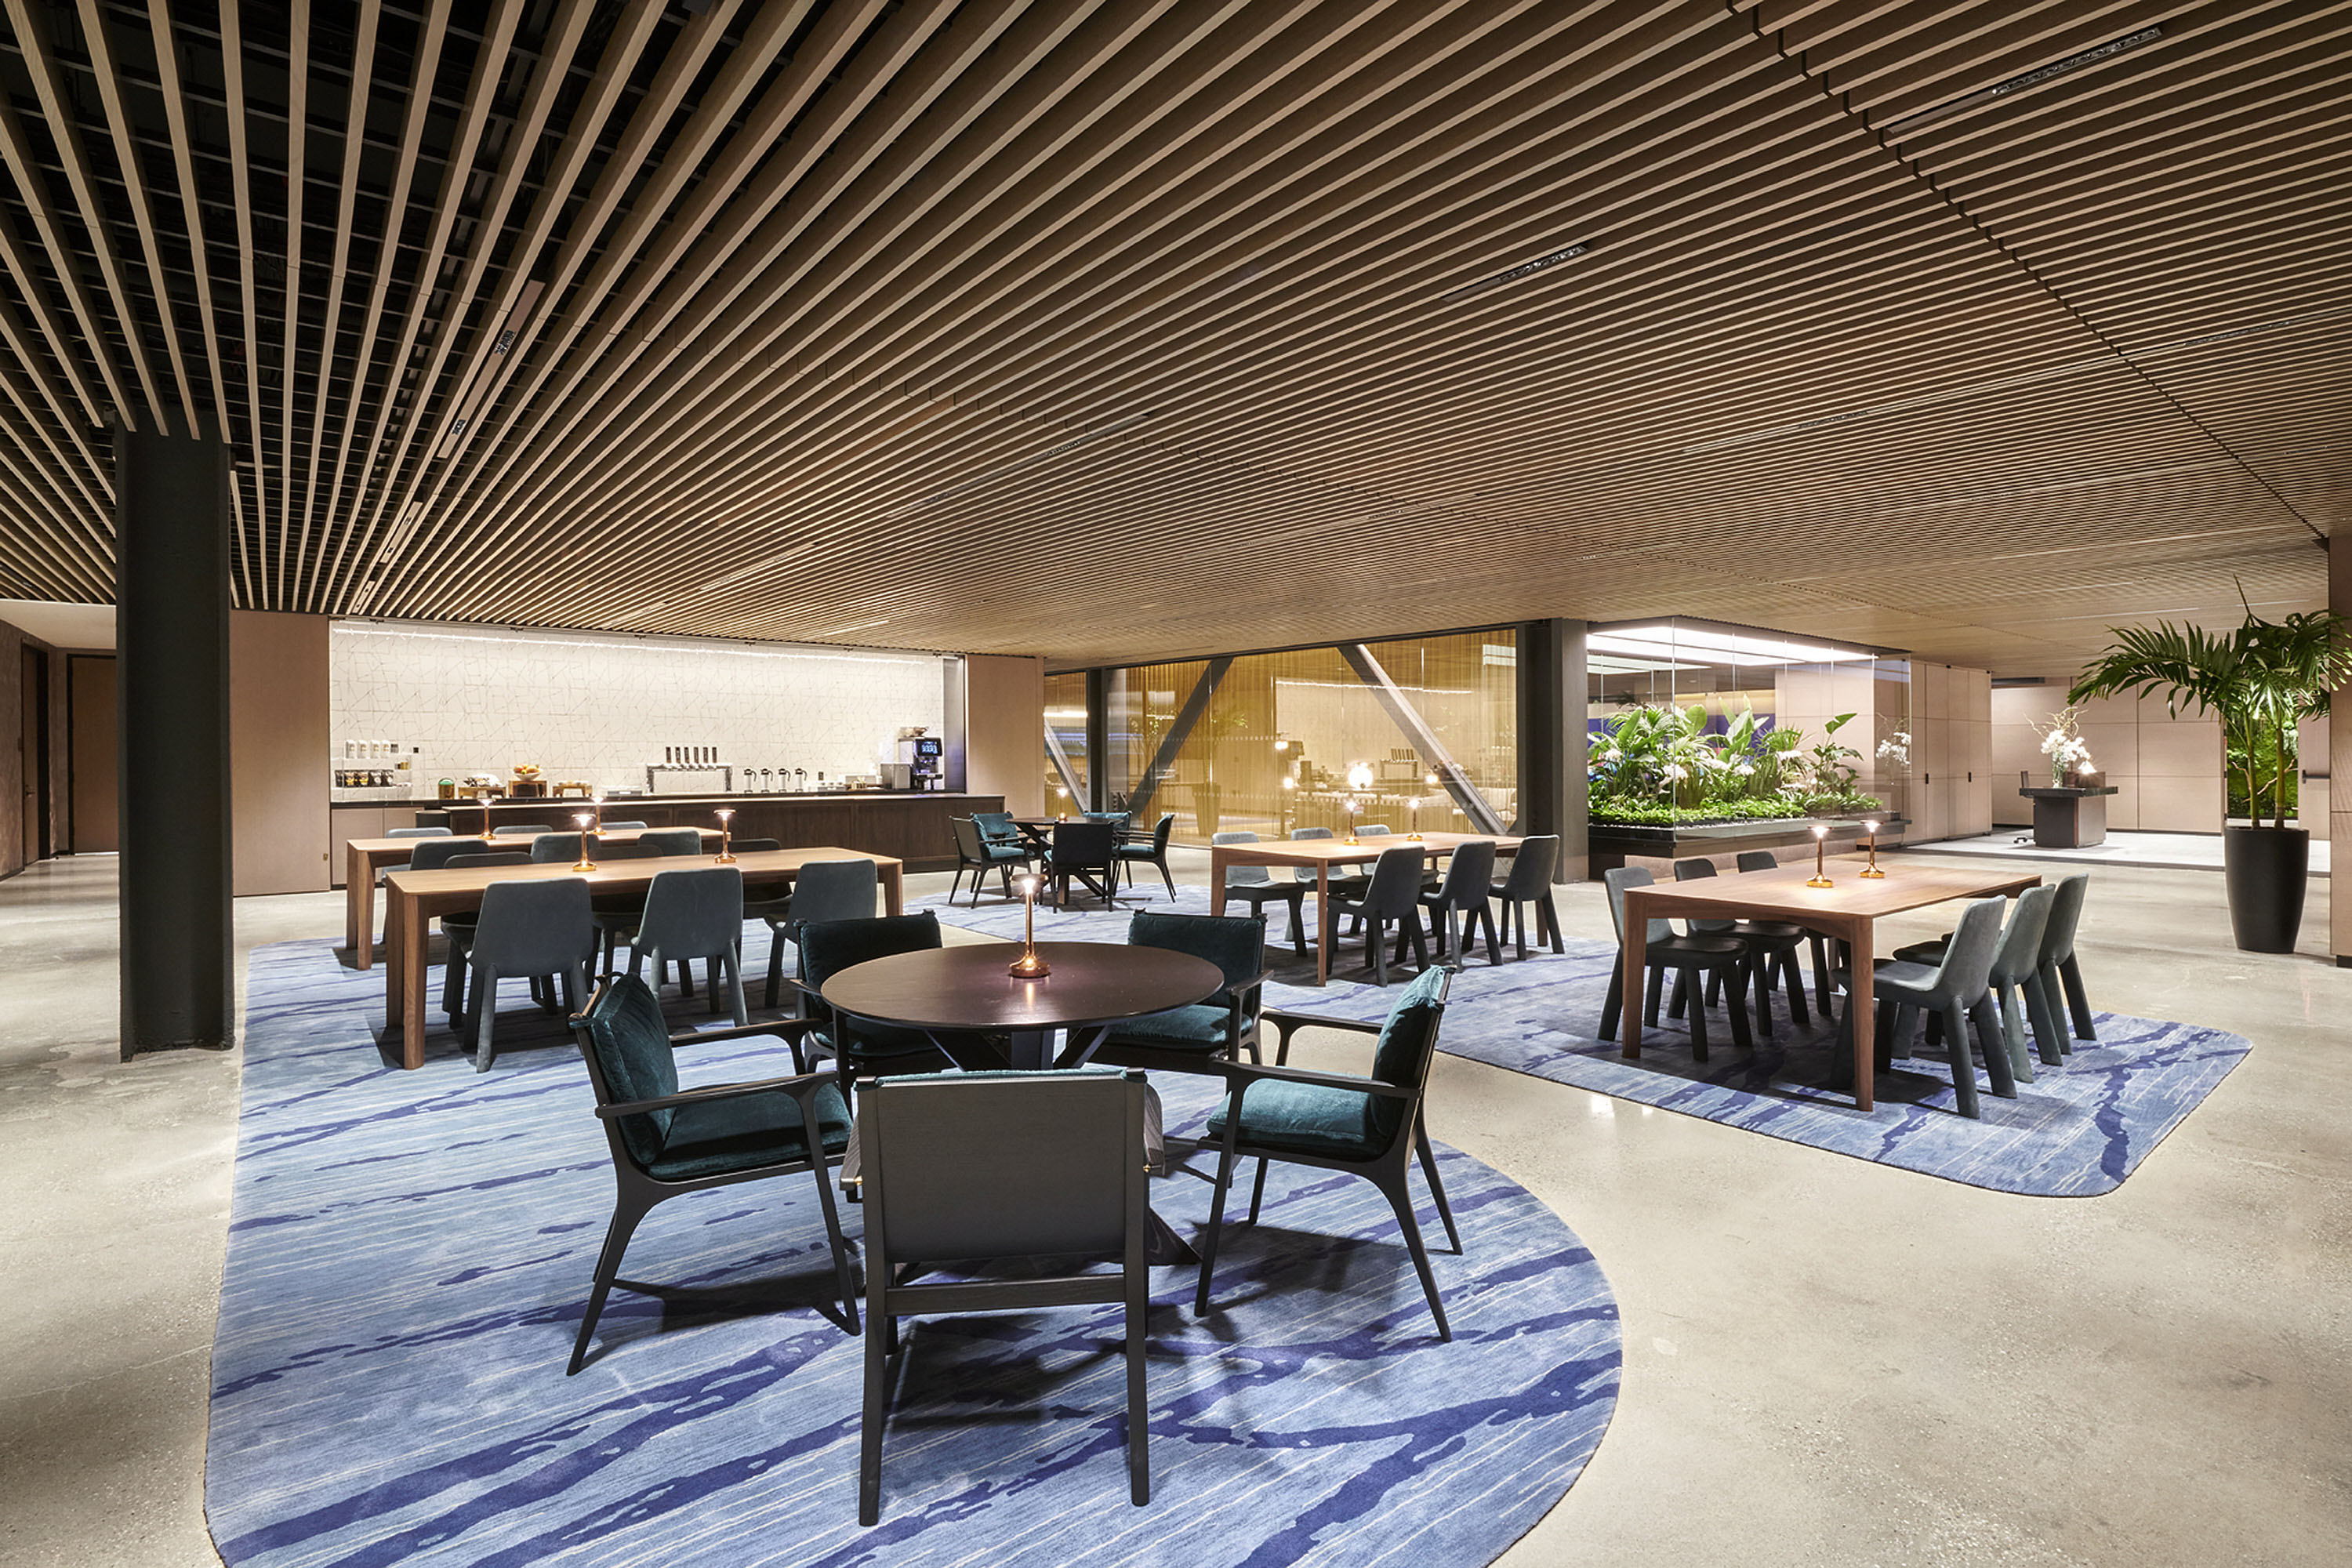
Ease 1345
About Clutch
Hyper-Niche Content
Our conferences are specific to niche sub-sets of the technology industry, drilling down into the biggest issues, challenges and market trends facing tomorrow's leaders.
Collaboration first
Enjoy ample networking opportunities, roundtable discussions, interactive group sessions and real-world case-studies that arm attendees with actionable insights.
Dynamic & Bite-Size formats
No more death-by-PowerPoint. Our events are short, sharp and collaborative with a variety of session formats and a 3/4 day commitment to ensure returns on your time investment.
Get In Touch
Contact our event team for any enquiry

Danny Perry
For sponsorship opportunities.

Lili Munar
For guest and attendee enquiries.

Steph Tolmie
For speaking opportunities & content enquiries.

Taylor Stanyon
For event-related enquiries.
Go deeper
The IT conferences in Australia worth a senior leader's time in 2027: CIO, AI, cyber, data, DevOps and government events, with typical dates and costs.
AI in government in Australia: DTA responsible AI policy v2.0, impact assessments, transparency statements, NSW AI Assessment Framework and procurement.
AI coding assistants for large engineering organisations: what the evidence says about productivity, and how to roll out, measure and govern them.