
Sydney Data Protection & Security Summit 2026
Join us at the third edition of the Data Protection & Security Summit, where industry experts and IT leaders for hands-on sessions, expert insights, and discussions on the latest in data protection and privacy.
Fortify your data security strategies.
We're bringing together security professionals, IT leaders, and industry experts to tackle the latest challenges in data protection and privacy.
Explore best practices for data encryption, loss prevention strategies, and balancing data accessibility with security. Learn about the Australian Data Privacy Act, data breach incident response, and how AI and ML are reshaping data security. Engage in interactive sessions, real-world case studies, panel discussions, and debates to stay ahead in the field of data protection.
Key Themes:
- The Evolving Landscape of Data Protection
- Australian Data Privacy Act
- Data Breach Incident Response
- Data Encryption Techniques
- Data Loss Prevention Strategies
- Balancing Data Accessibility and Security
- AI and ML in Data Security
- On-Prem vs. Cloud: What Offers Better Data Protection
Register now to secure your place!
Association Partner
Our Speakers









Agenda
Beat the rush and join us early for complimentary barista-made coffee and breakfast.
This session highlights how embedding privacy and security into organisational culture can drive customer trust and long-term business success beyond compliance.
- Strategies for fostering a privacy-first mindset across all levels of an organisation.
- Integrating privacy by design in products and services to achieve regulatory and market differentiation.
- Empowering cross-functional teams to proactively identify and mitigate data protection risks.
As organisations accelerate their adoption of generative AI, protecting sensitive information has become a critical business priority. Understanding how AI systems access, process, and interact with enterprise data is essential to balancing innovation with governance, security, and trust.
Key takeaways:
- Understand where AI creates data exposure risks by examining how generative AI tools ingest, process, and interact with enterprise information.
- Establish effective guardrails and governance frameworks to maintain control over sensitive data while enabling responsible AI adoption.
- Unlock AI-driven value with confidence through practical strategies that reduce risk, strengthen compliance, and support secure innovation at scale.
Threat volumes continue to rise, but most security teams are facing the same reality: limited resources and growing expectations. Leaders are being asked to detect threats faster, protect more sensitive data, and manage new AI-driven risks without expanding headcount or budgets. This panel brings together security and data leaders to share how they are strengthening resilience in practice, through smarter investment, targeted automation, and deeper collaboration across organisations.
We’ll explore:
- Where threat intelligence sharing genuinely improves security outcomes and where it simply creates more noise
- What security teams are automating today to reduce workload without weakening oversight
- How organisations and teams are collaborating across sectors to strengthen collective defence
- How leaders are building security cultures that enable teams to move faster under pressure
Governance, Risk, and Compliance functions face growing pressure to align with various standards and regulations. However, the diverse evidence expectations and review cycles can lead to fragmentation and heavy workloads. AI-driven approaches can now perform evidence analysis, extract relevant insights, validate control alignment, and detect gaps early, resulting in a more reliable, scalable, and high-performing GRC function that supports faster decision-making and stronger organisational resilience.
In this innovative session, attendees will be faced with a series of scenarios that they may face in their roles. Attendees will discuss the possible courses of action with their peers to consider the ramifications of each option before logging their own course of action.
Results will be tallied and analysed by our session facilitator and results will impact the way the group moves through the activity.
Will we collectively choose the right course of action?
As health and research agencies come under growing pressure to accelerate access to sensitive data, protecting patient privacy and data integrity remains a critical governance priority. The NSW Cancer Institute's CanDLE program demonstrates how sensitive data linkage; including decades of historical cancer registry records dating back to 1972, can be managed responsibly while still meeting the speed and scale researchers now demand.
We'll look at:
- Where sensitive data linkage creates security and compliance risk by examining how research access requests interact with historical and contemporary cancer registry records.
- Effective data governance frameworks to maintain long-term control over sensitive datasets while accelerating legitimate research access.
- Unlocking research-driven value confidently through practical strategies that manage historical data complexity, reduce risk, and support secure, scalable data sharing.
Compromised credentials remain a major entry point for attackers, but the window between account takeover and wider compromise is often where security teams can make the biggest difference. This session explores how organisations can detect identity compromise earlier, automate containment and accelerate investigations.
We'll Discuss:
- How security teams can identify unusual identity activity and recognise the early signs of account takeover.
- Where automated responses can quickly contain compromised identities before attackers move laterally.
- How security teams can reduce investigation time from days to hours by combining identity signals, attack patterns and automated workflows
Learn how organisations across sectors can integrate generative AI technologies while maintaining strong data protection and managing associated risks.
- Establishing governance frameworks and designated AI oversight roles to ensure responsible AI use.
- Implementing data classification and access controls to protect sensitive information during AI deployments.
- Collaborating with trusted AI vendors and conducting ongoing risk assessments to safeguard organisational data assets.
Select a topic of discussion and engage in an interactive roundtable discussion with a group of your like-minded peers.
Put your knowledge to the test in this fast-paced quiz covering real-world trivia, key concepts, and emerging trends. Compete for bragging rights - and a travel voucher - as the top scorer takes the crown.
As organisations increasingly rely on third-party data, AI models and external technology providers, the boundaries around data ownership, access and accountability are becoming more complex. This fireside chat will explore how organisations can share data with partners and AI providers while maintaining appropriate governance, security and control. The conversation will focus on the practical questions leaders should be asking before data is shared, AI systems are connected or third parties are given access to sensitive information.
- How should organisations assess what data is being shared with third parties, where it is going, how it will be used and whether it could be combined with other data or used to train AI models?
- When an AI system, cloud provider or external partner is handling organisational data, how should accountability be divided? What governance, contractual and oversight mechanisms are needed to maintain control?
- What practical guardrails can organisations put in place around third-party AI use, data access and model development while still enabling teams to experiment, collaborate and move quickly?
Key Points:
- What is “context” and how is it implemented?
- Context includes both industry-based and organisational specific artefacts.
- What are “information assets” and how do we identify, maintain them, and make them useful?
- Capturing, representing, and securing organisational knowledge
- Making organisational knowledge accessible to AI (and humans) for better generation of relevant, timely, and accurate output.
Educational apps are increasingly embedded in Australian schools, handling sensitive information about children, their learning and their digital behaviour. But how well do their privacy policies reflect what these apps actually do in practice?
Drawing on research into the security and privacy of children’s educational apps used in Australian schools, this keynote examines what happens when you look beyond the promises made in privacy policies and investigate how software behaves in the real world. It explores what these findings reveal about data collection, information sharing, security practices and the challenges of understanding what happens to data once it enters third-party applications.
Key discussion points:
- How investigating the actual behaviour of educational apps can uncover discrepancies between stated privacy practices and what happens in practice, including data collection, tracking and information sharing.
- What the research reveals about the challenges of assessing software security and privacy, particularly when applications handle sensitive information about children and other vulnerable users.
- Practical lessons for organisations on testing software behaviour, scrutinising third-party providers, validating privacy claims and strengthening oversight throughout the application lifecycle.
As AI adoption accelerates, workforce and operational data are increasingly repurposed for analytics and training models, blurring the line between what’s technically possible and what’s ethically acceptable.
With growing scrutiny and regulations, leaders must balance innovation, compliance, and employee trust, and decide; Just because we can use the data, should we?
This interactive session puts these questions directly to the audience. Participants vote live on a series of real-world scenarios, explore the results together, and vote again as perspectives shift through the discussion.
- Can internal employee data be used to train AI models without explicit consent?
- What level of de-identification is “safe enough” for AI analytics?
- How transparent should organisations be about AI data use?
- Who should own decisions on AI data ethics and privacy?
- When innovation conflicts with privacy risk, what should win?
Unwind with your peers for a couple of drinks on us!
Our event sponsors



Past Speaker Highlights




Past Sponsors
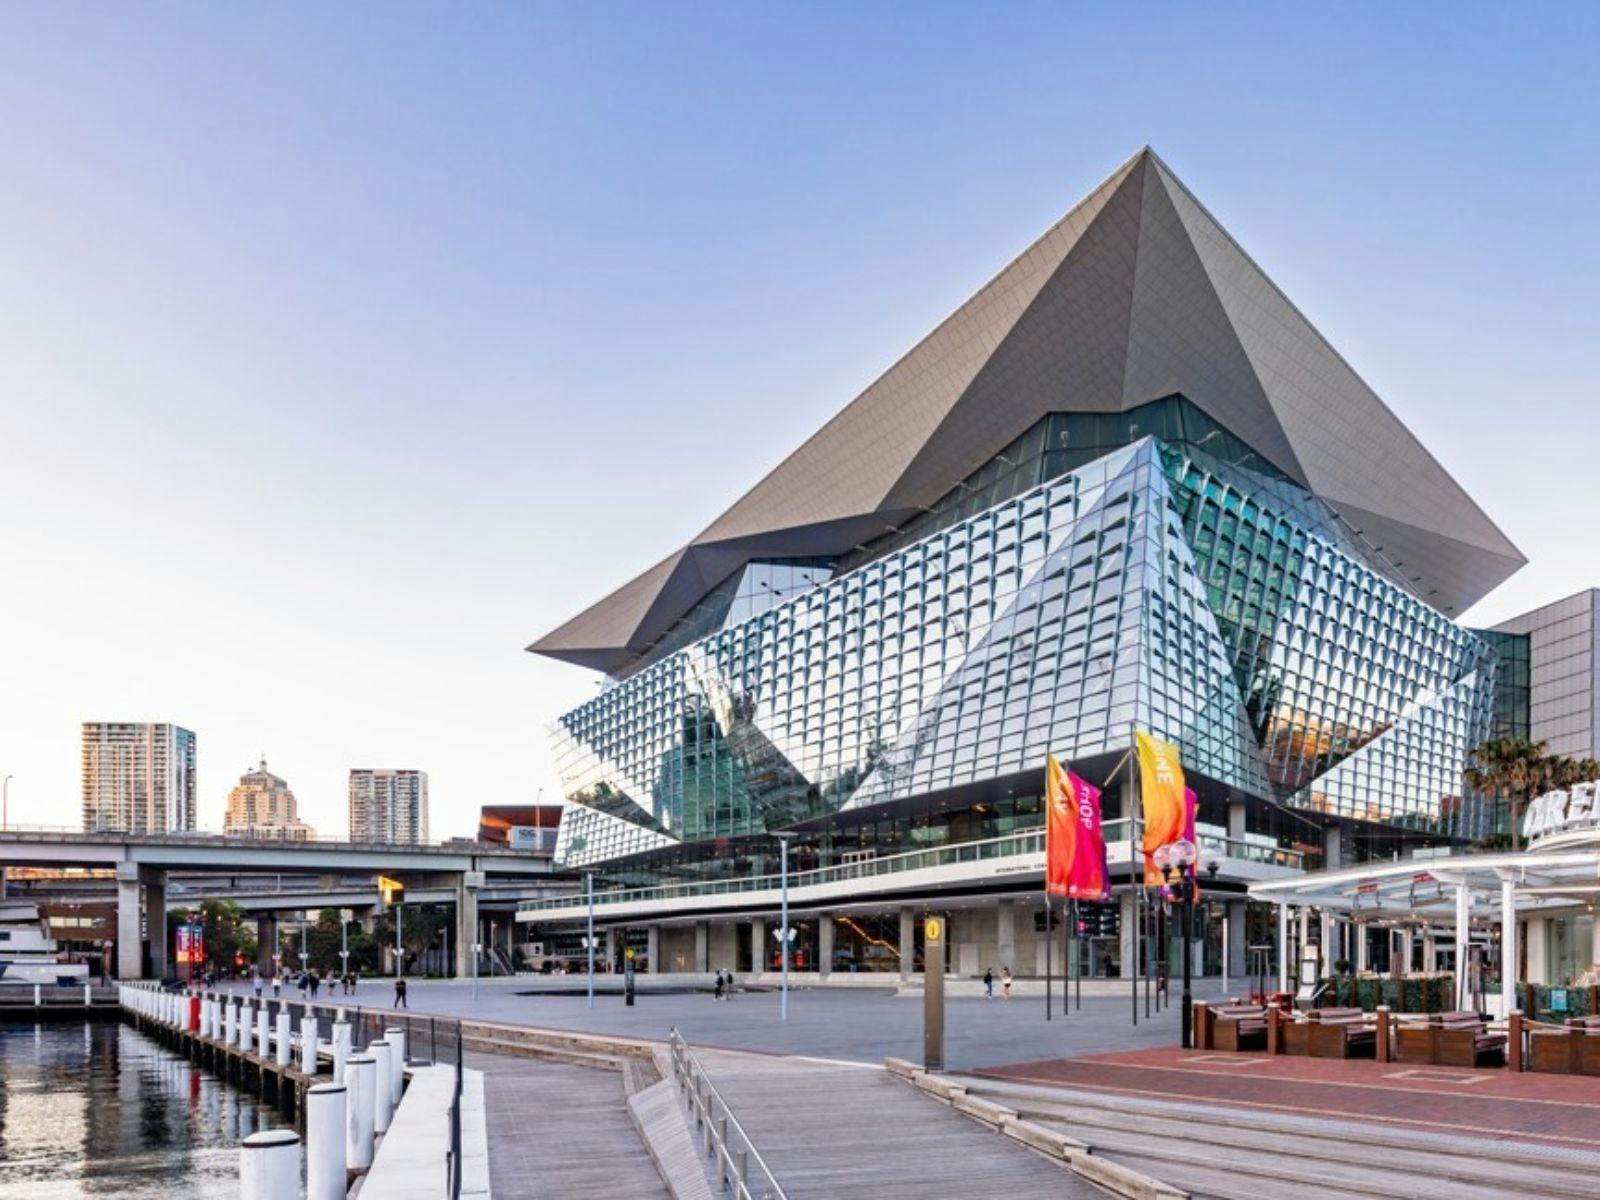
Event Location
ICC Sydney, Parkside Ballroom, Level 2
About Clutch
Hyper-Niche Content
Our conferences are specific to niche sub-sets of the technology industry, drilling down into the biggest issues, challenges and market trends facing tomorrow's leaders.
Collaboration first
Enjoy ample networking opportunities, roundtable discussions, interactive group sessions and real-world case-studies that arm attendees with actionable insights.
Dynamic & Bite-Size formats
No more death-by-PowerPoint. Our events are short, sharp and collaborative with a variety of session formats and a 3/4 day commitment to ensure returns on your time investment.
Get In Touch
Contact our event team for any enquiry

Danny Perry
For sponsorship opportunities.

Lili Munar
For guest and attendee enquiries.

Steph Tolmie
For speaking opportunities & content enquiries.

Taylor Stanyon
For event-related enquiries.
Go deeper
The IT conferences in Australia worth a senior leader's time in 2027: CIO, AI, cyber, data, DevOps and government events, with typical dates and costs.
AI in government in Australia: DTA responsible AI policy v2.0, impact assessments, transparency statements, NSW AI Assessment Framework and procurement.
AI coding assistants for large engineering organisations: what the evidence says about productivity, and how to roll out, measure and govern them.